Inside a Motherboard: UEFI Security Research, the Slow Way - Part 1
A laptop firmware security research series written by someone who was completely confused at the start, still gets confused regularly, and is currently winning anyway. If you are here because you wanted to research a laptop chip but had no idea which laptop to buy or what to do with it, this series is for you.
The series so far:
| Part | Title | Status |
|---|---|---|
| 1 | Three Boards, One Repair Shop, and a 32 MB Secret | Three Boards, One Repair Shop, and a 32 MB Secret |
| 2 | I Dumped a 32 MB BIOS and Found Four Worlds in It | Coming soon |
| 3 | Boot Guard: The Signature Wall Before the BIOS | Coming soon |
| 4 | dTPM vs PTT: The Chip and the Ghost | Coming soon |
| 5 | Sniffing the TPM: Watching a Secret Cross a Wire | Coming soon |
The part nobody talks about: the doubt
Every security blog starts after the interesting part. They never show you the weeks of sitting and staring at a shopping cart, asking yourself stupid questions like:
- Should I buy a new laptop or a used one?
- Is this board too new? Too old?
- Will I break it? (Yes. Plan for it.)
- How much is too much money to pay for something I am going to possibly fry?
- Does anyone even sell the schematic for this thing?
This is called the laptop shopping doubt, and it is real. It is also completely normal, and it is the reason so many people never start. They cannot pick the board, so they pick nothing.
Here is the truth I landed on after all the doubt. For firmware research, you do not want the newest shiny laptop. You want three things:
- Old enough that the schematic and boardview are floating around the internet. A 2019 board has free PDFs and CAD files. A 2026 board has a DMCA.
- Cheap enough to break. You WILL put clips on chips, you WILL short things, you WILL brick one. It should not cost you rent.
- Boring enough that people have dumped its BIOS a thousand times. The more dumps exist, the more you can compare yours against. Comparison is how you learn.
That logic is how I ended up with three boards instead of one. Which brings me to the confusion that became my method.
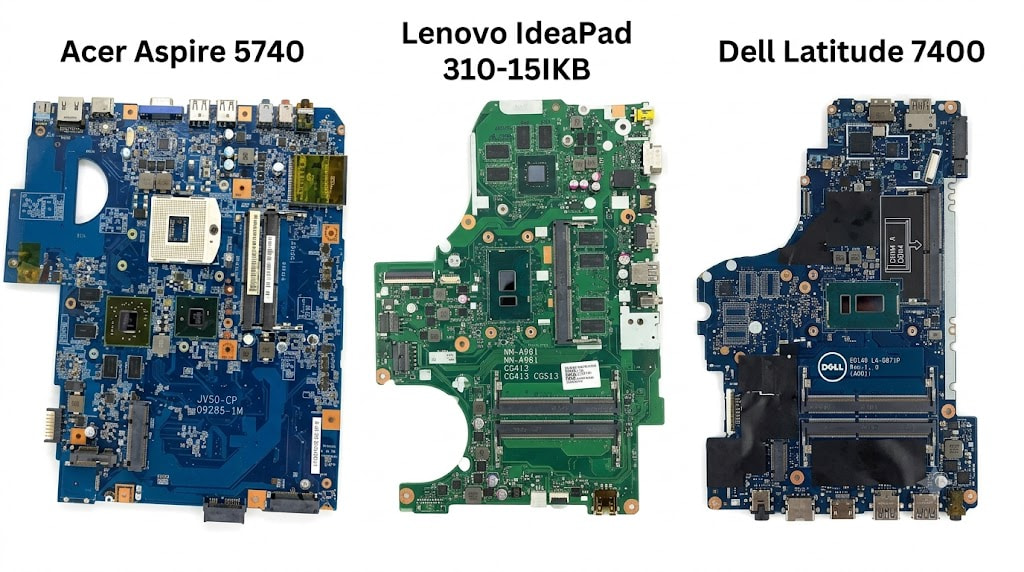
The repair shop ping-pong (and why I have three boards)
My primary research board is a Lenovo. It is also, at this exact moment, at a repair shop. It has spent more time at that shop than on my desk. Every time I make a plan, someone hands the laptop back, or takes it away. It is a ping-pong match between the shop owner and my research, and nobody told me the rules.
So while the Lenovo was going back and forth, I needed something else to practice on. That is how the research actually became three boards at once:
- Acer Aspire 5740 (2010) - my sacrificial board. Old enough to be a dinosaur, slow enough that nobody cared. This is the board I am allowed to ruin. It has zero TPM, zero Boot Guard, and two separate flash chips. It is the “learn to walk” board.
- Lenovo IdeaPad 310 (2017) - the primary target. Currently in the shop, obviously. When I do get it back, I have to finish hunting its EC chip marking before it gets stolen away again.
- Dell Latitude 7400 (2019) - the boss board. This one turned out to be the surprise. A corporate laptop with an actual physical TPM chip on it, full schematic, full boardview, and a 32 MB BIOS dump that matches my laptop’s exact board revision.
I did not plan to get three boards. The repair shop planned it for me, by taking my laptop in and out constantly. So if your board keeps disappearing, do not wait for it. Work on another board. The confusion worked out fine.
Reading chips by squinting
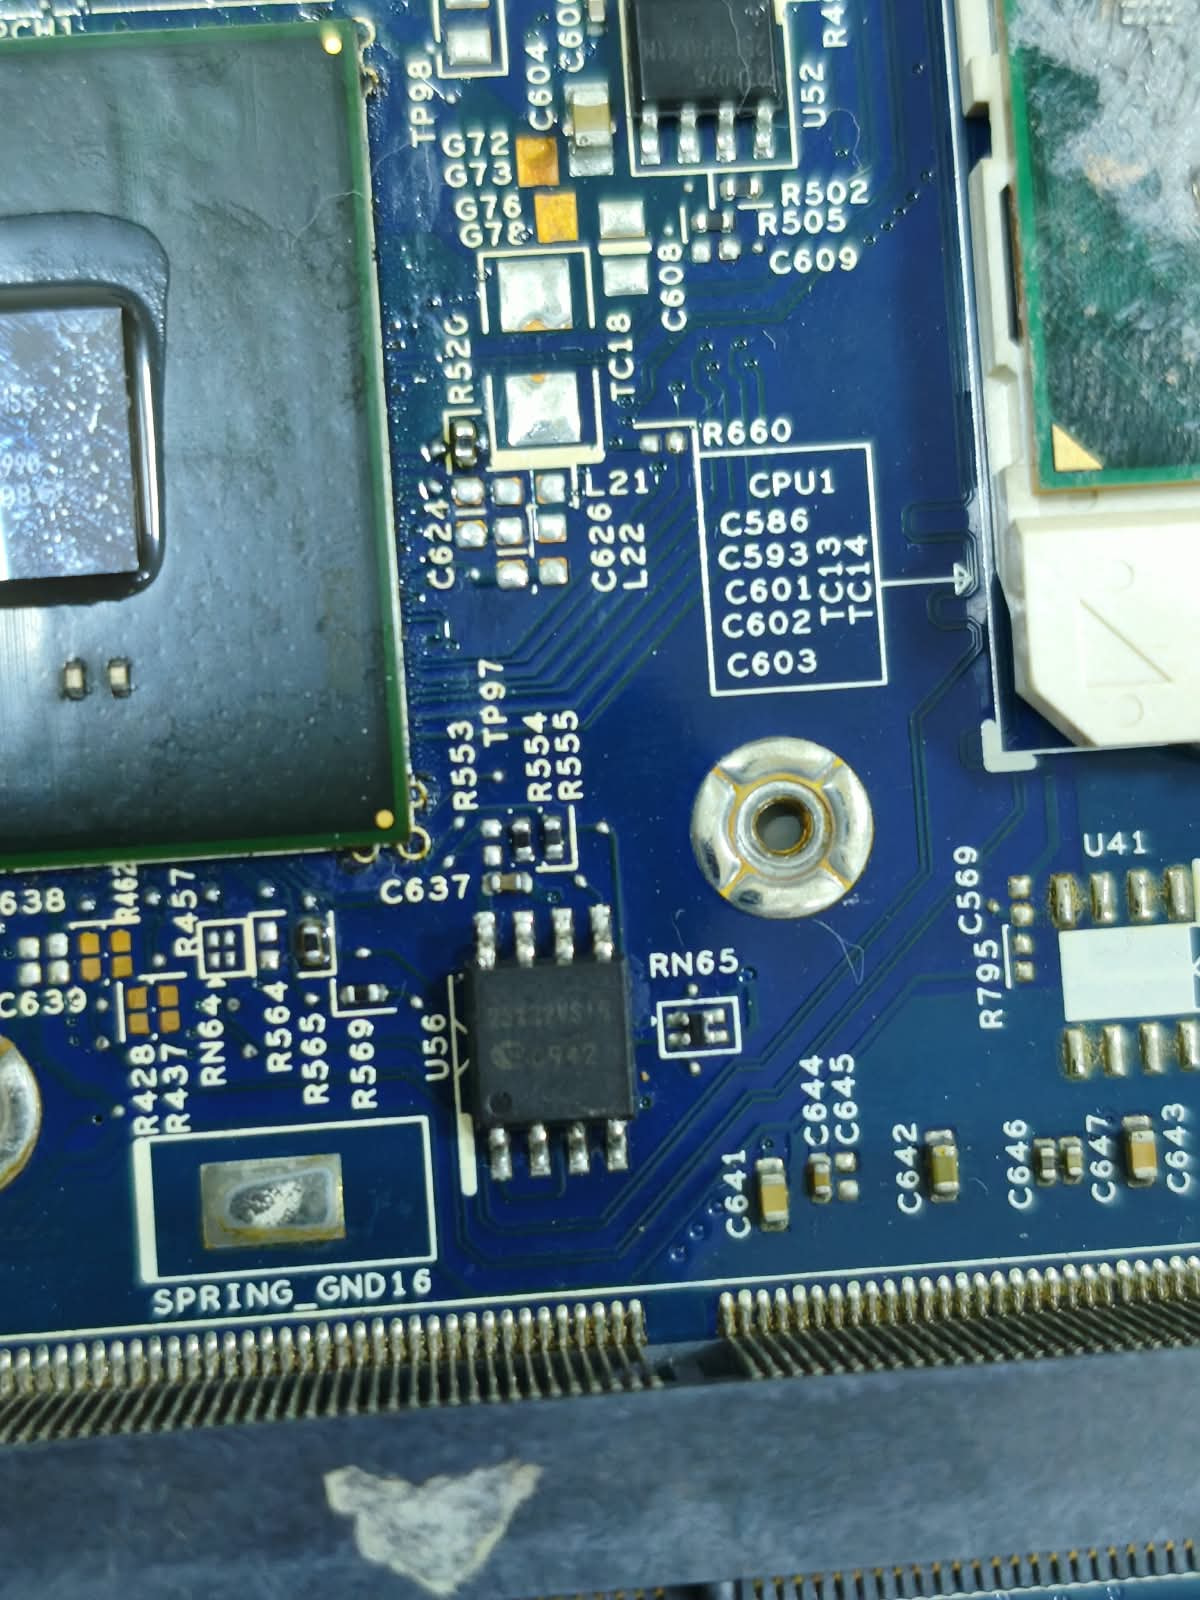
Nobody warns you that reading a chip marking is harder than reading the datasheet. The part numbers are insanely small. I do not have a macro camera setup, so I read every marking with my own two eyes, bent over the board, sometimes with a magnifier, basically squinting.
It went wrong immediately. I read a flash chip as 28X32VS18. It was actually W25X32VSIG. The “W” at the start just… looks like a “2” when the chip is tilted. I learned that “W” stands for Winbond by literally asking a hardware guy to re-read it for me. Embarrassing, but that is how it works. You do not trust your eyes. You check twice, or you ask someone with better eyes.
There are two kinds of chip numbers at play here, and understanding the difference clears up half the mess:
- The chip part number (like
W25X32VSIGorGD25B64CSIG) tells you what the chip is, how big it is, and which company made it. - The CPU stepping marking (like
SR2ZV) tells you the exact model of the processor.SR2ZV= Intel Core i7-7500U. Every laptop processor has one of these codes, and they are on a public Intel list. It is like a cheat sheet.
I also learned the SOIC-8 pinout by heart because it is the same on almost every BIOS flash chip:
       ┌───U───┐
 CS#  1│●      │8  VCC
  DO  2│       │7  HOLD#
 WP#  3│       │6  CLK
 GND  4│       │5  DI
       └───────┘
Pin 1 has a dot next to it. Find the dot first. Everything else falls into place. WP# and HOLD# on pins 3 and 7 usually go through a tiny resistor to VCC, which is the “please protect me” wiring. We will come back to those pins; they matter for write protection.
The download that was worth paying for
Here is a question nobody tells you to ask: where do you get a BIOS dump to study when you still have not dumped your own chip?
The answer is the repair forums. badcaps, the telly places. People physically pull flash chips off laptops with a programmer and upload the raw content. For a board as common as this Dell, the dumps exist. Some of them are behind a small paid membership, and honestly, it was the best money I spent in this whole project. One fee, and I got:
- A full 32 MB BIOS dump for my exact board (LA-G871P Rev 1.0 A00)
- The boardview file (a CAD map of every component)
- The schematics as PDFs
- The block diagram
Before trusting any downloaded file, I checked its SHA-256. A hash is just a fingerprint for a file. The forum posted the hash of the dump, I ran the download at a terminal, and the fingerprint matched. That sounds boring, but it is the difference between analyzing a genuine dump and analyzing somebody’s half-edited “fixed ME” firmware. It matched, so I kept it.

Funny detail: the Linux box I did this on has no monitor. I managed to get the command line working, and when I tried to open the UEFI GUI tool, it refused because there is no graphical display. So I used the command-line extraction tool instead, which printed the whole flash layout as plain text. When your computer is nicer than your monitor, the terminal saves you.
The 32 MB that holds four worlds
Reading a flash dump is like opening a suitcase full of other suitcases. My Dell’s entire 32 MB chip splits into four regions, and each one is a separate world:
| Region | Start | Size | What lives in it |
|---|---|---|---|
| Descriptor | 0x00000000 | 4 KB | The map of everything. Which regions exist, where they sit, who gets to read/write them |
| EC | 0x00001000 | 1 MB | The embedded controller firmware. The little brain that runs fans, keyboard, power buttons |
| ME | 0x00101000 | ~15 MB | The Intel Management Engine. A whole secret computer running inside your Intel CPU |
| BIOS | 0x01000000 | 16 MB | The actual firmware you boot. UEFI, the drivers, everything |
Add them up: 4 KB + 1 MB + 15 MB + 16 MB = 32 MB. It all fits exactly, no gaps. That is how you know the dump is a clean, full chip read.
Here is the part I found genuinely interesting. On my old 2010 Acer, the EC firmware lived on its own separate little flash chip. On this 2019 Dell, the EC firmware lives inside the main flash chip, in its own dedicated region. The industry moved the EC brain into the big chip. Same for the ME. So when you dump the main chip of a modern laptop, you get BIOS + ME + EC + the map, all in one 32 MB file. On the 2010 board, I had to touch two chips. On the Dell, it is one. Fewer chips to clip, even more secrets per chip.
The chip and the ghost
This is the discovery that surprised me the most, and it is not finished yet.
The Dell board has a real, physical TPM chip on it. A Trusted Platform Module. I found it, read the marking, ST33HTPH2032AHD1, searched it, and it is a discrete TPM 2.0 made by STMicroelectronics. Security chips live on the board. Their whole job is storing secrets like BitLocker keys and refusing to let software steal them.
But wait. When I dug through the 32 MB dump, I found that the Intel Management Engine has a firmware-based TPM built in. It is called PTT (Platform Trust Technology). So the same laptop has TWO TPMs available: the physical chip (ST33) and the ghost inside the firmware (PTT/Intel).
Here is the twist. The laptop decides which one is actually working. The operating system only ever talks to one TPM. And which one it picks matters hugely for security research, because the physical chip talks over a little wire bus that you can physically touch and sniff with a logic analyzer. The ghost inside the firmware has no wire to sniff. It is inside the CPU.
So my research question right now is literally: is this laptop using the chip, or the ghost? I have the physical chip marked in my notes, and the PTT firmware spotted inside the dump, and the answer to who wins is going to decide whether the TPM sniffing experiment at the end of this series is possible. The detection is one command away on the actual laptop, and I have not run it yet. This is the part that is unfinished, and I am leaving it on purpose. Research is mostly unfinished questions.
A wall made of signatures
I also went looking for Boot Guard, and I found it fully populated in the dump:
- A Boot Guard ACM (Authentication Code Module) sitting in the flash
- A Key Manifest (the crypto key chain)
- A Boot Policy Manifest, which lists which parts of the BIOS are allowed to boot
- A SHA-256 hash of the initial boot block, basically a cryptographic fingerprint of the first things that run
Finding all of that in the image is one thing. Proving the laptop actually enforces it at power-on is another. That enforcement flag does not live in the dump. It lives in a CPU register that the processor checks on boot, and I need a running laptop to read it. Another unfinished question. Presence of a wall in the blueprint is not proof the wall stands.
These two threads, the chip vs the ghost and the enforcement of Boot Guard, are exactly the kind of thing that makes this whole project fun. The dump is a snapshot. The laptop is the movie. You need both, and the laptop is currently… at the repair shop. Of course it is.
What is done and what is not
To keep myself honest, because blogs usually skip this:
Done.
- Picked the research boards (passed the shopping doubt, mostly).
- Identified all three boards, chips, CPU, EC.
- Dumped (acquired + hash-verified) a 32 MB BIOS for the Dell.
- Mapped the four regions: Descriptor, EC, ME, BIOS.
- Found the ST33 physical TPM chip on the board.
- Found PTT (firmware TPM) inside the ME.
- Found Boot Guard structures in the image.
Not done.
- Confirming which TPM this laptop actually uses (chip or ghost).
- Confirming Boot Guard is enforced at runtime (CPU register check).
- The TPM bus sniffing experiment.
- The Lenovo board: still at the shop. Still need its EC chip marking. It will be back. It always comes back, then leaves again.
For anyone who is still in the doubt phase
If you are still staring at a shopping cart wondering whether to start this whole thing: pick the cheapest old board with free schematics, buy a clip and a programmer, and plan for one board to die. The research does not need a perfect board. It needs a board that is present. Even the disappearing ones count, because they teach you to keep moving and work on the next board while the shop haggles over yours.
The doubt is the hardest part and it is the part nobody writes about. So consider this the blog nobody wrote before: start with doubt, pick a cheap board, and let your board vanish and reappear as many times as it wants. It all becomes material eventually.
What we learned
- Laptop shopping doubt is normal, and the fix is cheap and old with good documentation.
- Chip markings like
SR2ZVdecode to exact CPU models;W25X32VSIGdecodes to exact flash chips. Read them with a magnifier and ask someone to double check. - SOIC-8 pinout: pin 1 has a dot; CS#, DO, DI, CLK, WP#, HOLD#, VCC, GND, always the same order.
- SHA-256 is a file fingerprint; matching it means your downloaded dump is the same file the forum posted.
- A 32 MB laptop flash is four regions: Descriptor, EC, ME, BIOS. The EC moved from its own chip into the main flash on modern boards.
- dTPM and PTT: a laptop can have a physical TPM chip and a firmware TPM at the same time, and we still need to find out which one is actually active.
- Boot Guard structure in a dump is provisioned; actual enforcement is a runtime CPU state you verify on the live laptop.
Part 2 of this series goes inside the 32 MB dump, region by region, byte by byte, with the actual tools and outputs. Subscribe or just refresh the page until it appears. I am going to keep working until the repair shop runs out of excuses.